AI-Driven Managed Detection and Response (MDR)
A Stronger Security Posture, Together.
A Different Approach to MDR. Built Around Evidence, Not Just Alerts.
HAWK Network Defense strengthens security operations by connecting your existing security investments with AI-driven investigation, validated decisions, and coordinated containment.
Get more from the security tools you already own while accelerating investigation, coordinating response, and reducing the risk of business disruption.
Security Operations Built for Machine Speed.
From Detection to Evidence-Driven Decisions and Coordinated Response.
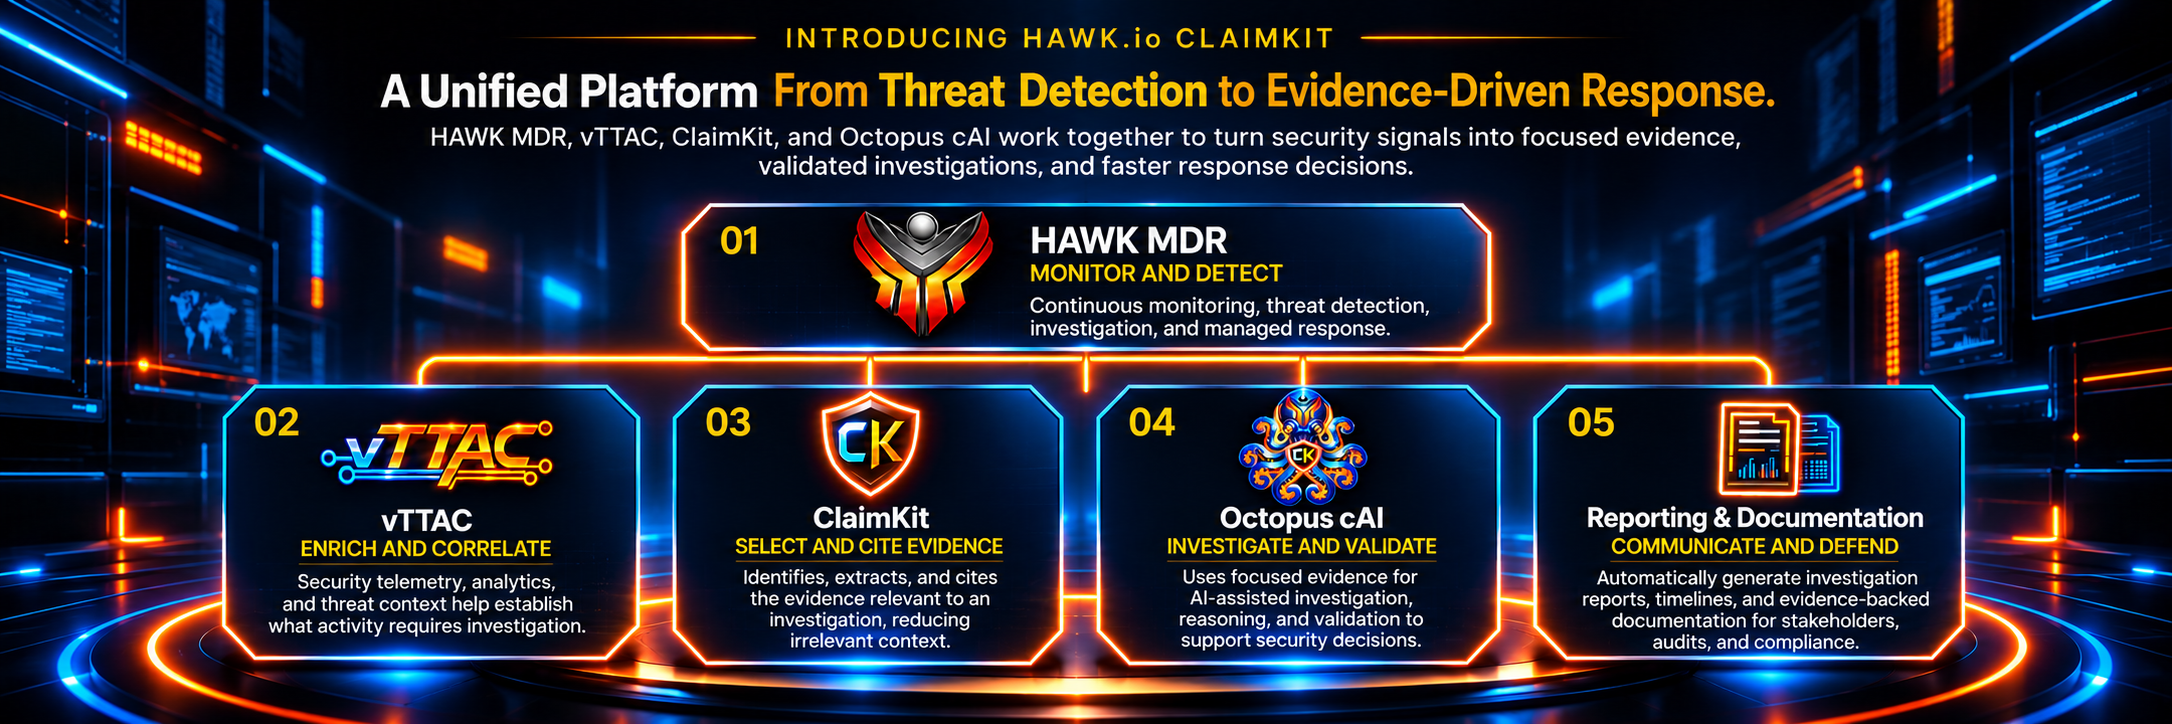
HAWK.io MDR connects security telemetry, host evidence, streaming analytics, and AI-driven investigation into a coordinated security operations process.
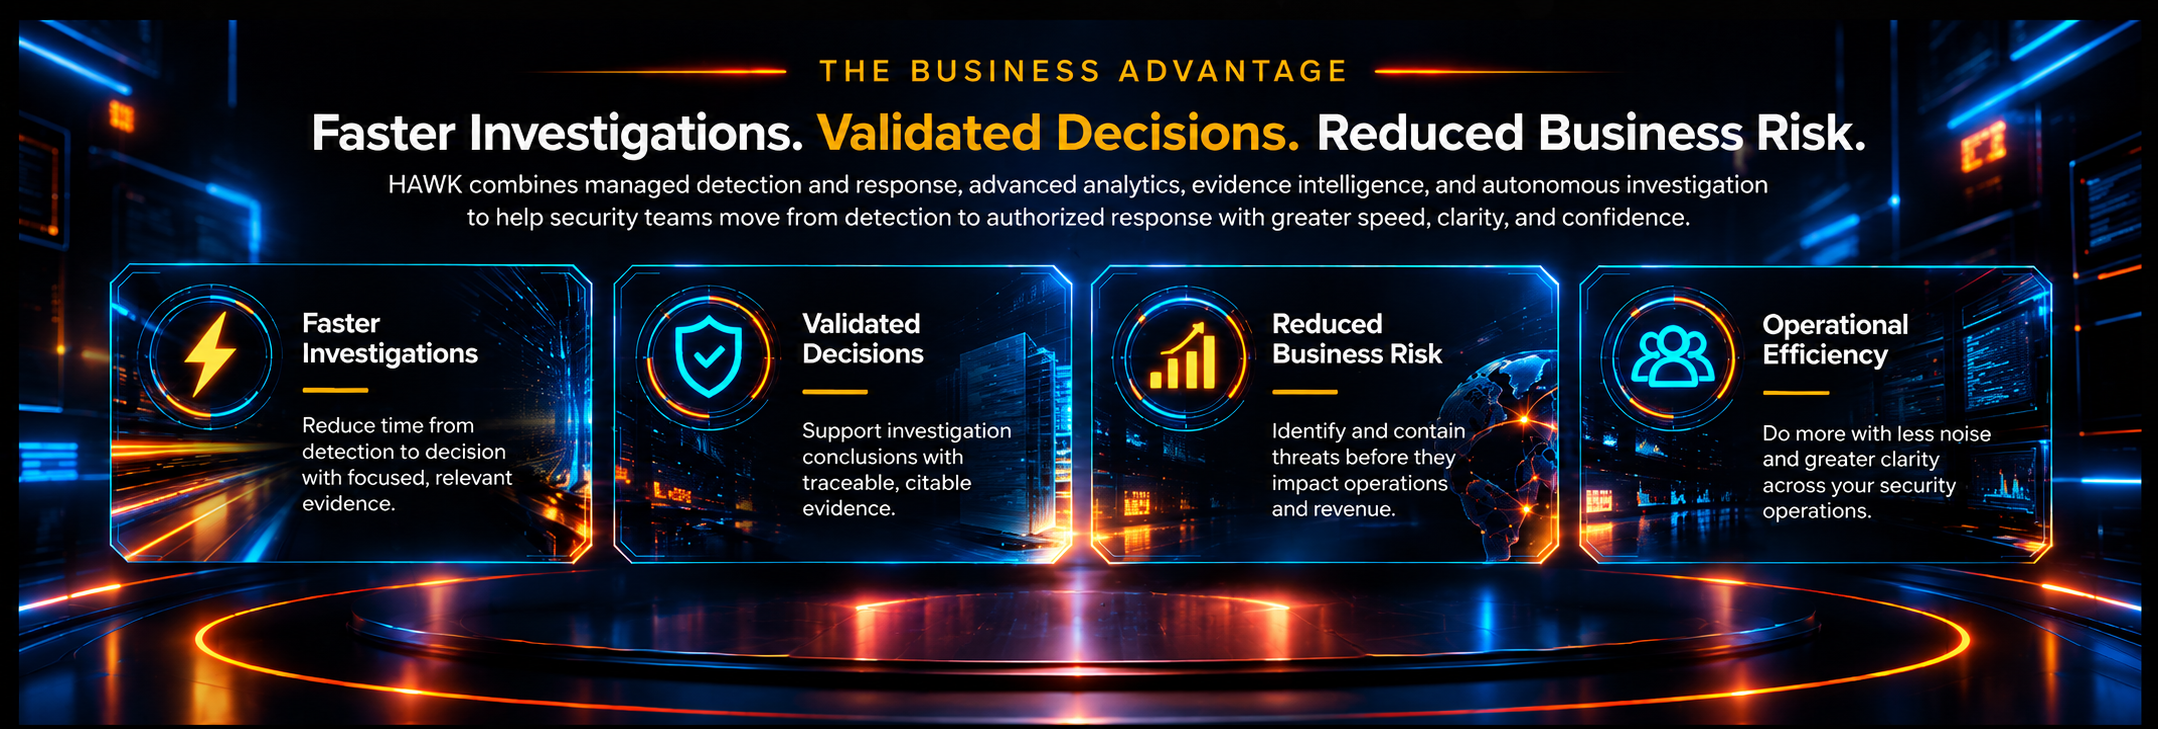
Rather than relying on disconnected alerts and sequential investigations, HAWK is designed to accelerate the progression from detection to validated decisions and authorized containment.
The result is a more connected operating model that helps security teams investigate efficiently, act with greater confidence, and make better use of their existing security investments.
HAWK vTTAC: Independent Endpoint Evidence - Compliments EDR
HAWK vTTAC provides independent endpoint telemetry and investigative evidence, complementing the protection you already have.
Improve the operational value of your security ecosystem without assuming that every existing tool must be replaced.
Extend Your Existing SIEM
Make more of the security investments you already have.
HAWK.io MDR is designed to complement existing security technologies by connecting available telemetry and evidence into a more coordinated investigation and response process.
Evidence-Driven Investigations - AI Retrieval Layer ClaimKit vs RAG
Move from alerts to defensible conclusions.
HAWK combines host evidence, streaming analytics, and AI-driven investigation to help establish what happened, why it matters, and which actions are justified.
The focus is on relevant evidence, traceable findings, and decisions that can withstand scrutiny.
HAWK ClaimKit supports this evidence-driven approach by identifying, extracting, and citing relevant investigative evidence, helping analysts work from focused, traceable information.
Compare ClaimKit (patent pending) with traditional RAG to see how ClaimKit outperforms RAG in evidence accuracy and efficiency.
See How ClaimKit (Patent Pending) Outperforms Traditional RAG
AI-Driven Decision Layer - Investigation and Coordinated Response
Accelerate action without surrendering control.
HAWK's security operations approach connects validated investigation findings with coordinated response under defined customer authority.
Octopus cAI supports AI-driven investigation and decision-making, helping security teams move from evidence to appropriate action.
The objective is to reduce unnecessary delays while maintaining appropriate safeguards, operational oversight, and verification of containment outcomes
Put HAWK MDR to Work in Your Environment
Talk with HAWK about your security operation’s needs, the tools you already use, and where investigation or response slows down.
Explore how HAWK Managed Detection and Response (MDR) could support your team.
“The first MDR platform that actually closes the loop on active threats.”
— STEVE ZALEWSKI
Former CISO, Levi Strauss
Built Around Real Security Operations
Technology should improve how security teams operate—not simply generate more alerts.
HAWK focuses on connecting detection, investigation, and response so customers can make informed security decisions and act with greater confidence.