Security Operations Built for
Machine Speed
HAWK.io is a security operations platform designed to reduce the time between detecting suspicious activity and taking authorized action. HAWK.io brings together real-time telemetry, contextual enrichment, evidence intelligence, autonomous investigation, policy-governed response, and expert security support in one coordinated operating model.
Rather than replacing the security technologies organizations already own, HAWK.io connects and operationalizes existing endpoint, identity, cloud, network, SIEM, and other security capabilities—turning security signals into evidence, decisions, and coordinated action.
Built on more than 100 years of combined security operations experience.
Engineered for Machine-Speed Security Operations.
OCTOPUS cAI + CLAIMKIT™
Evidence intelligence. Autonomous investigation. Coordinated action.
“The first platform that actually closes the loop on active threats.”
— STEVE ZALEWSKI
Former CISO, Levi Strauss
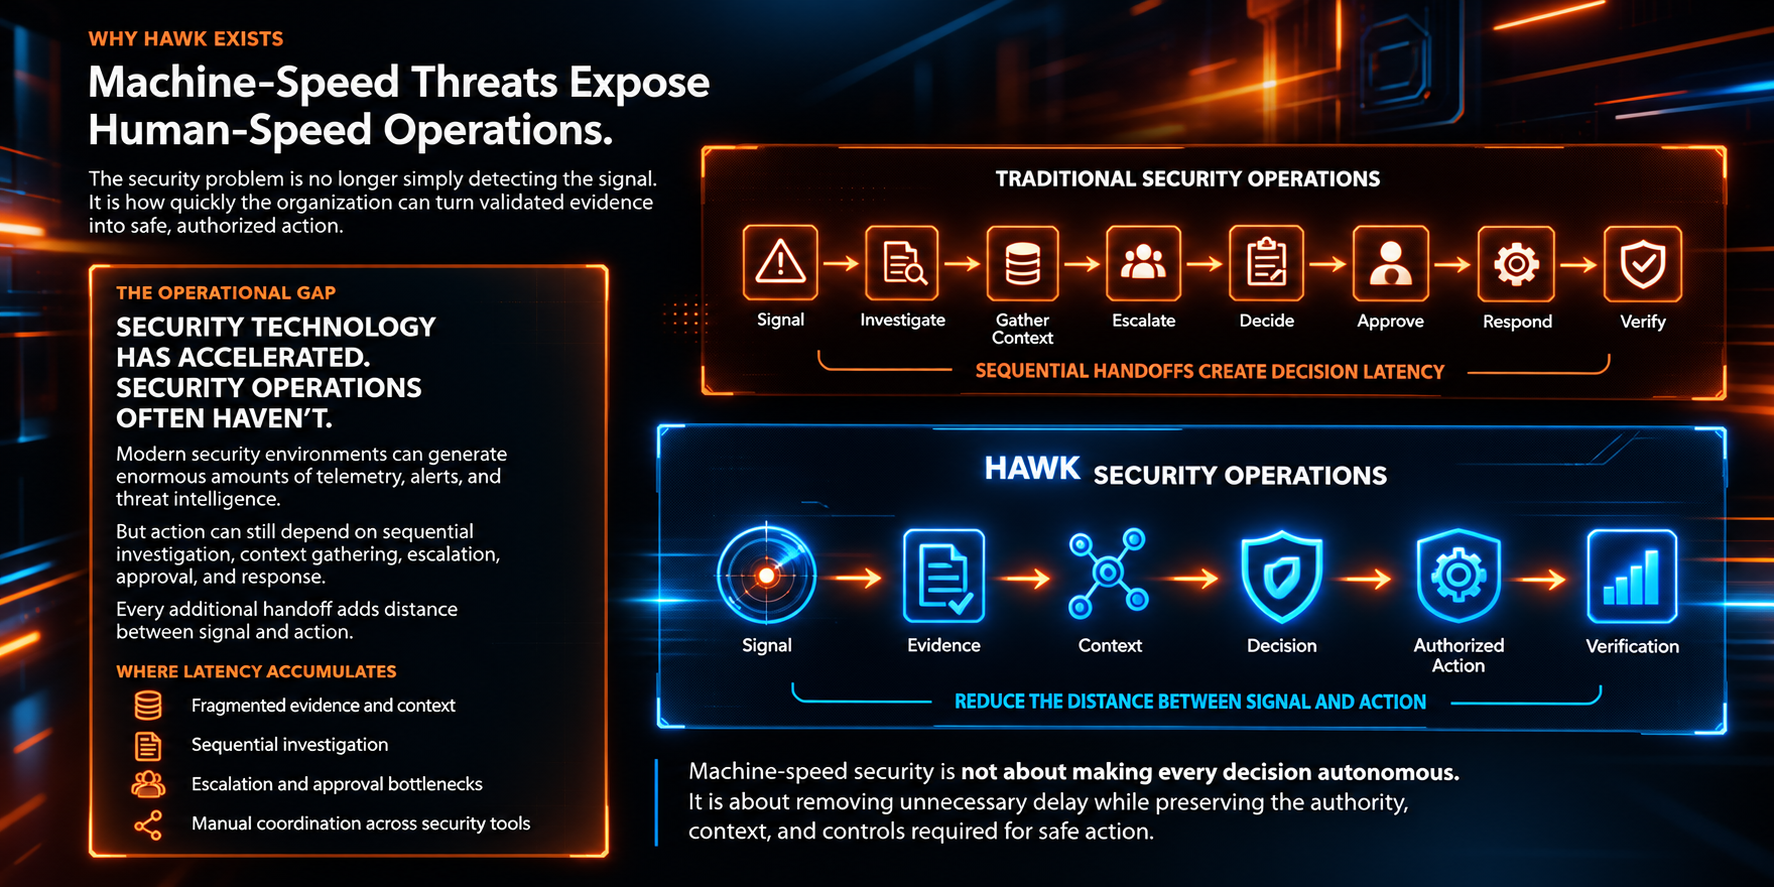
Reduce Decision Latency Across Security Operations
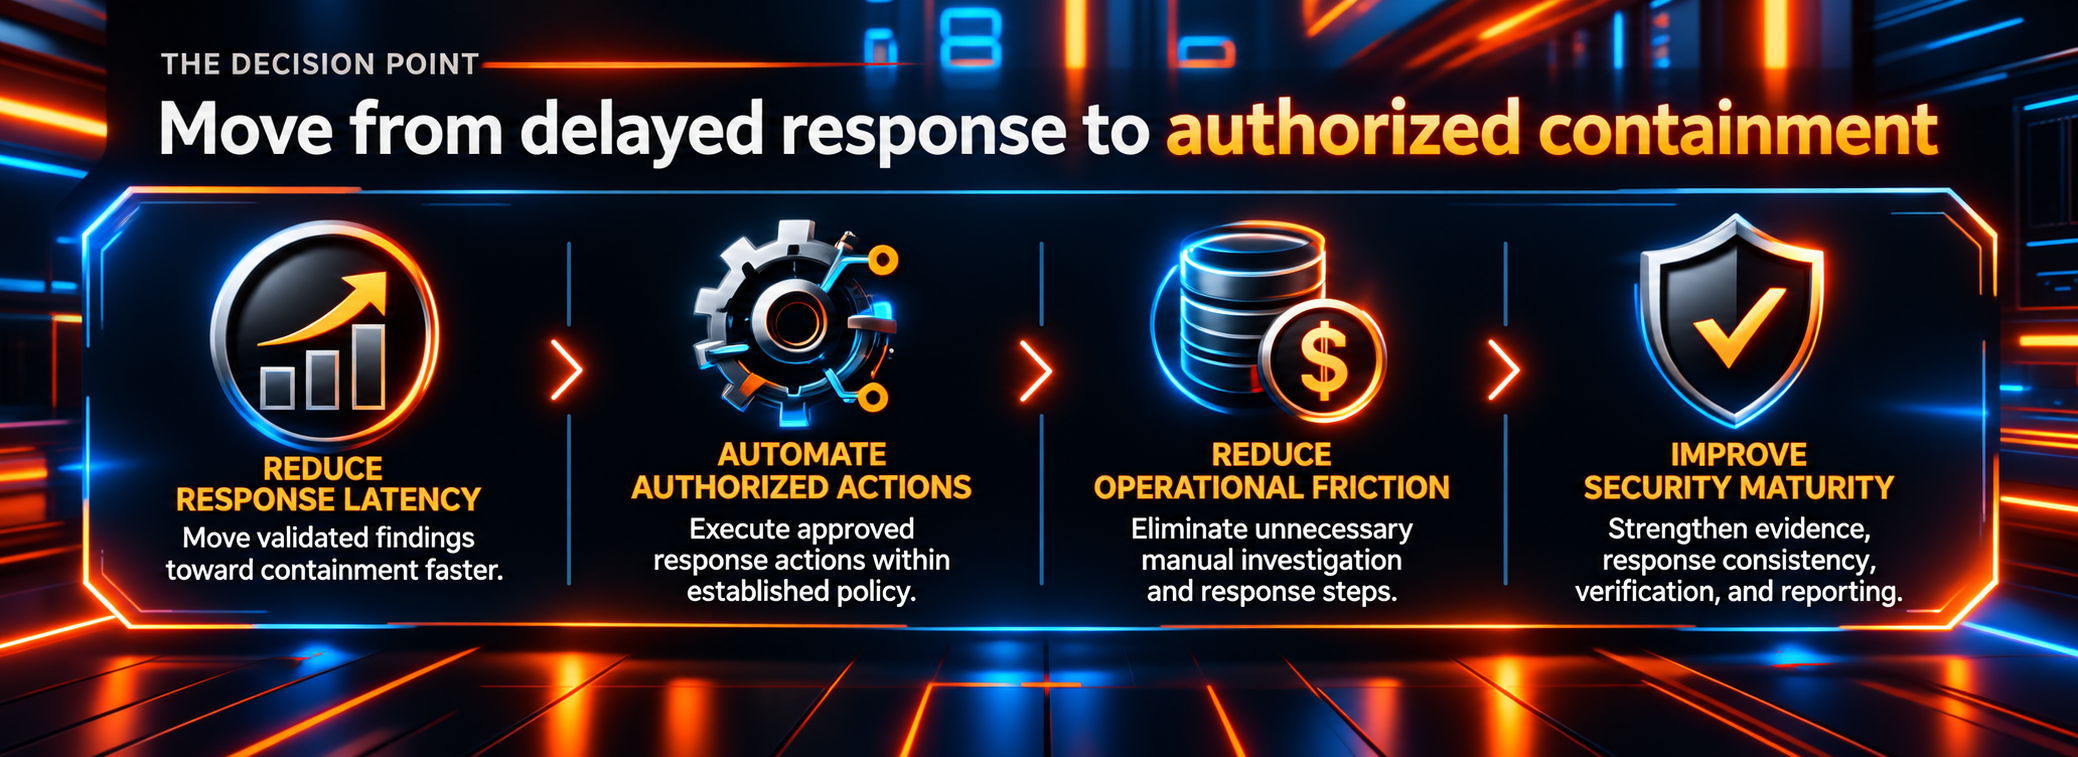
Modern security teams have more telemetry, alerts, and security tools than ever, but investigation and response can still be slowed by fragmented evidence and context, sequential investigation, escalation and approval bottlenecks, and manual coordination across security tools.
HAWK.io reduces that operational friction by moving security operations from signal → evidence → decision → authorized action → verification.
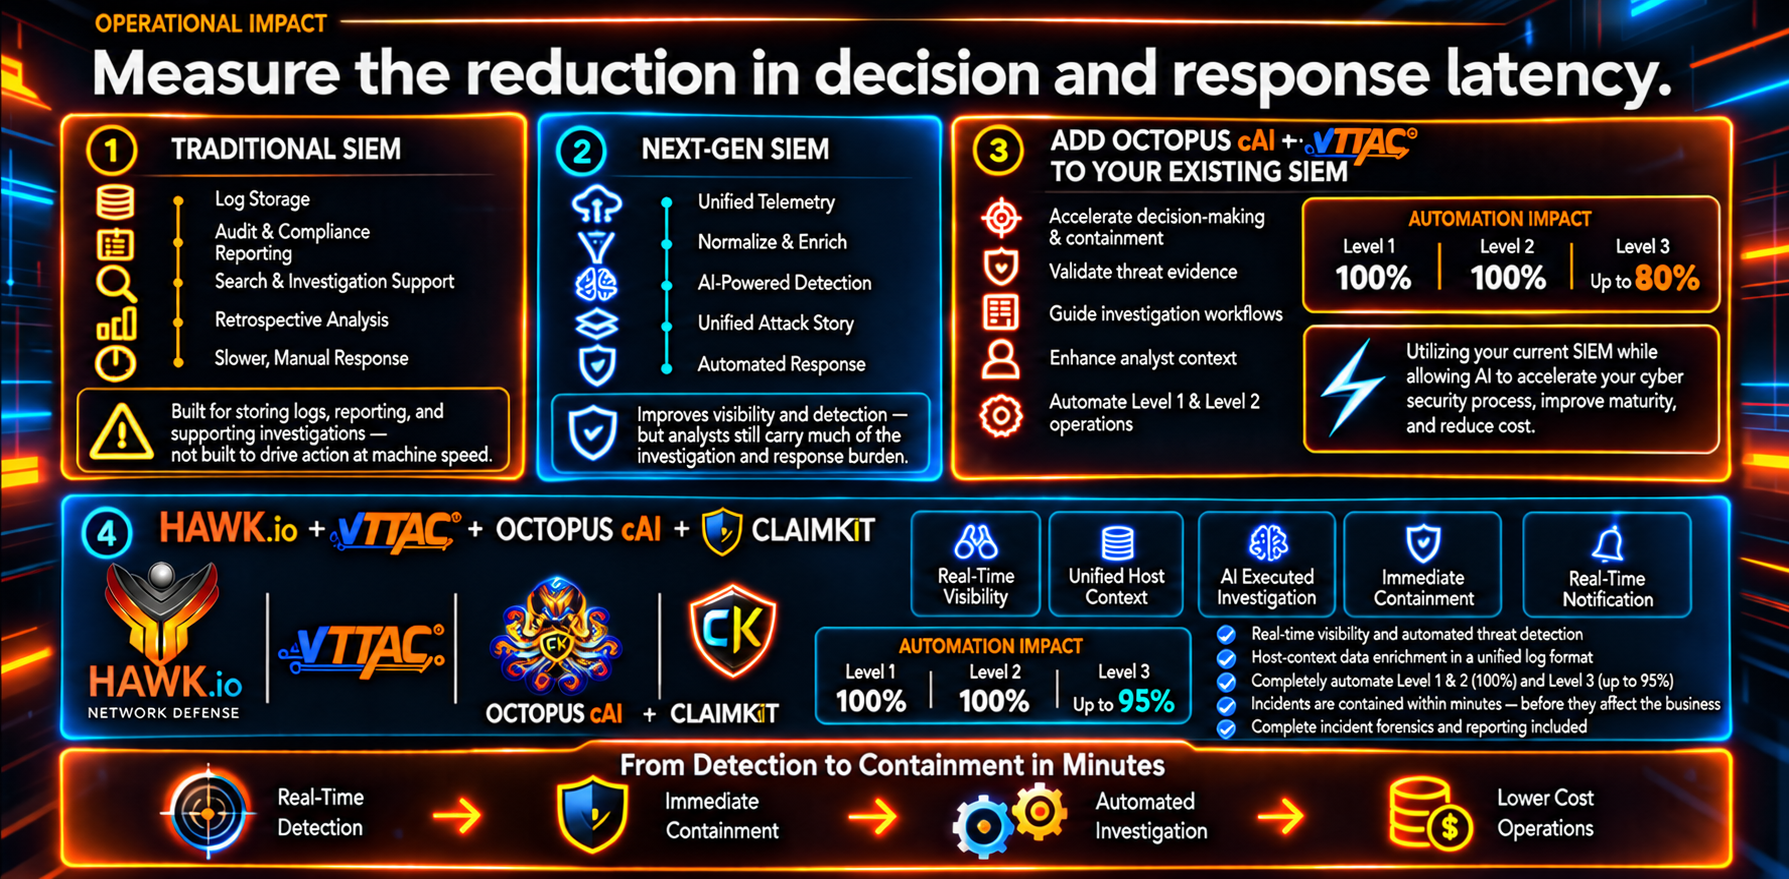
Extend Your Existing SIEM With Machine-Speed Security Operations
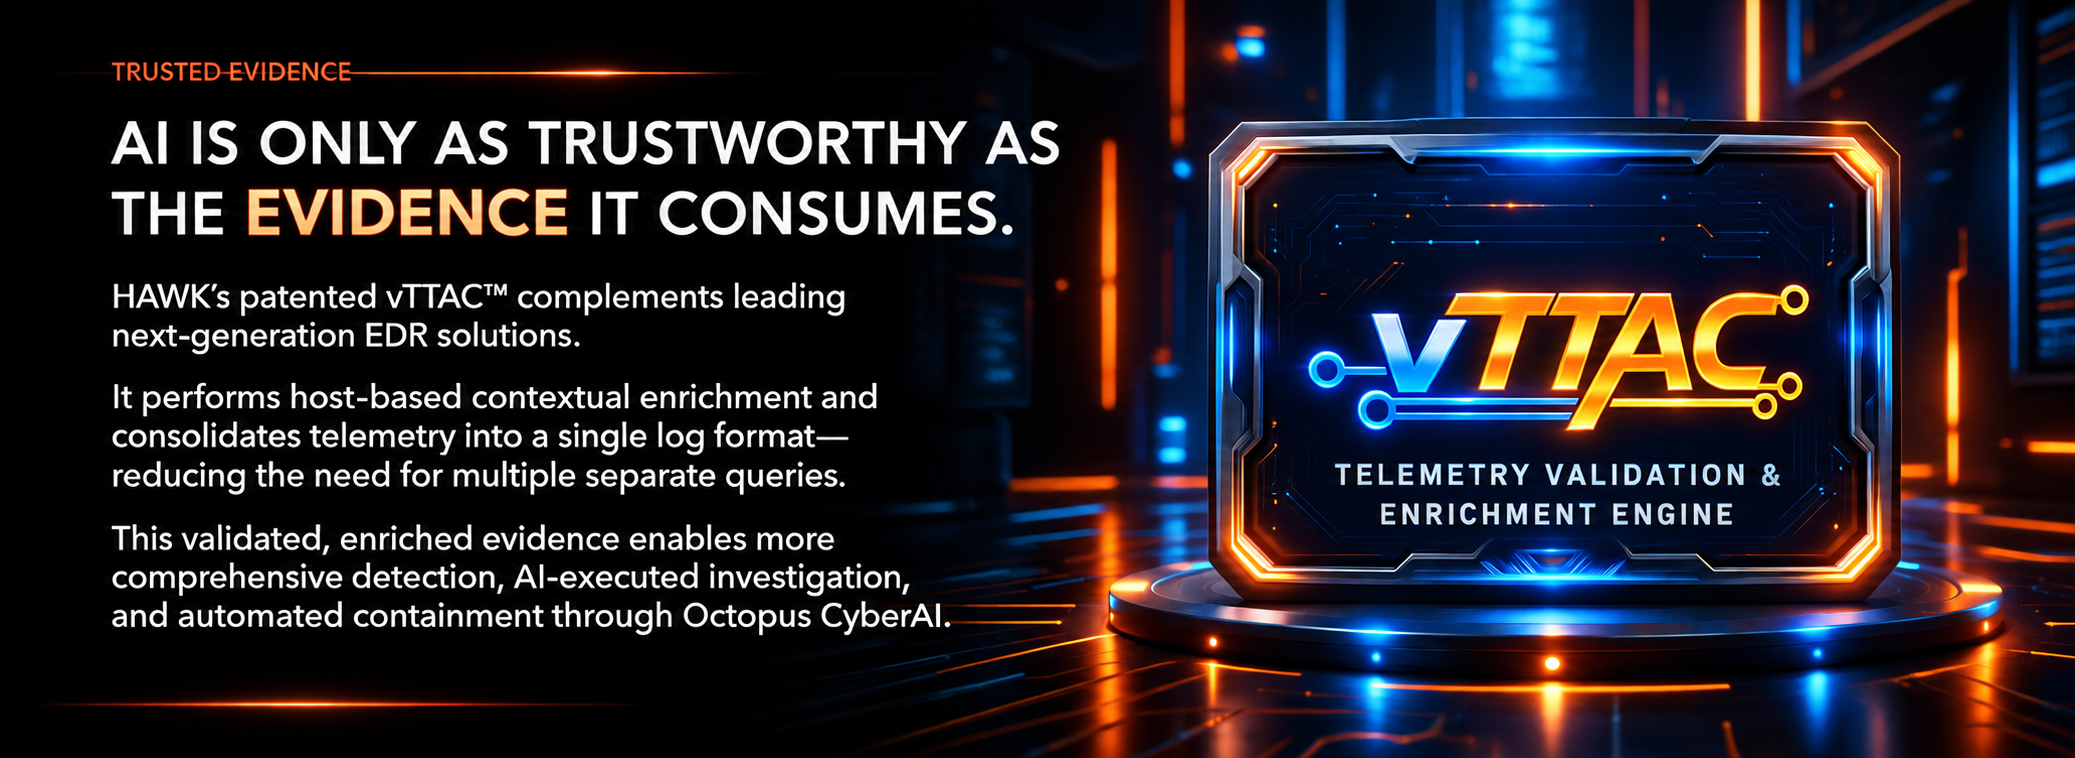
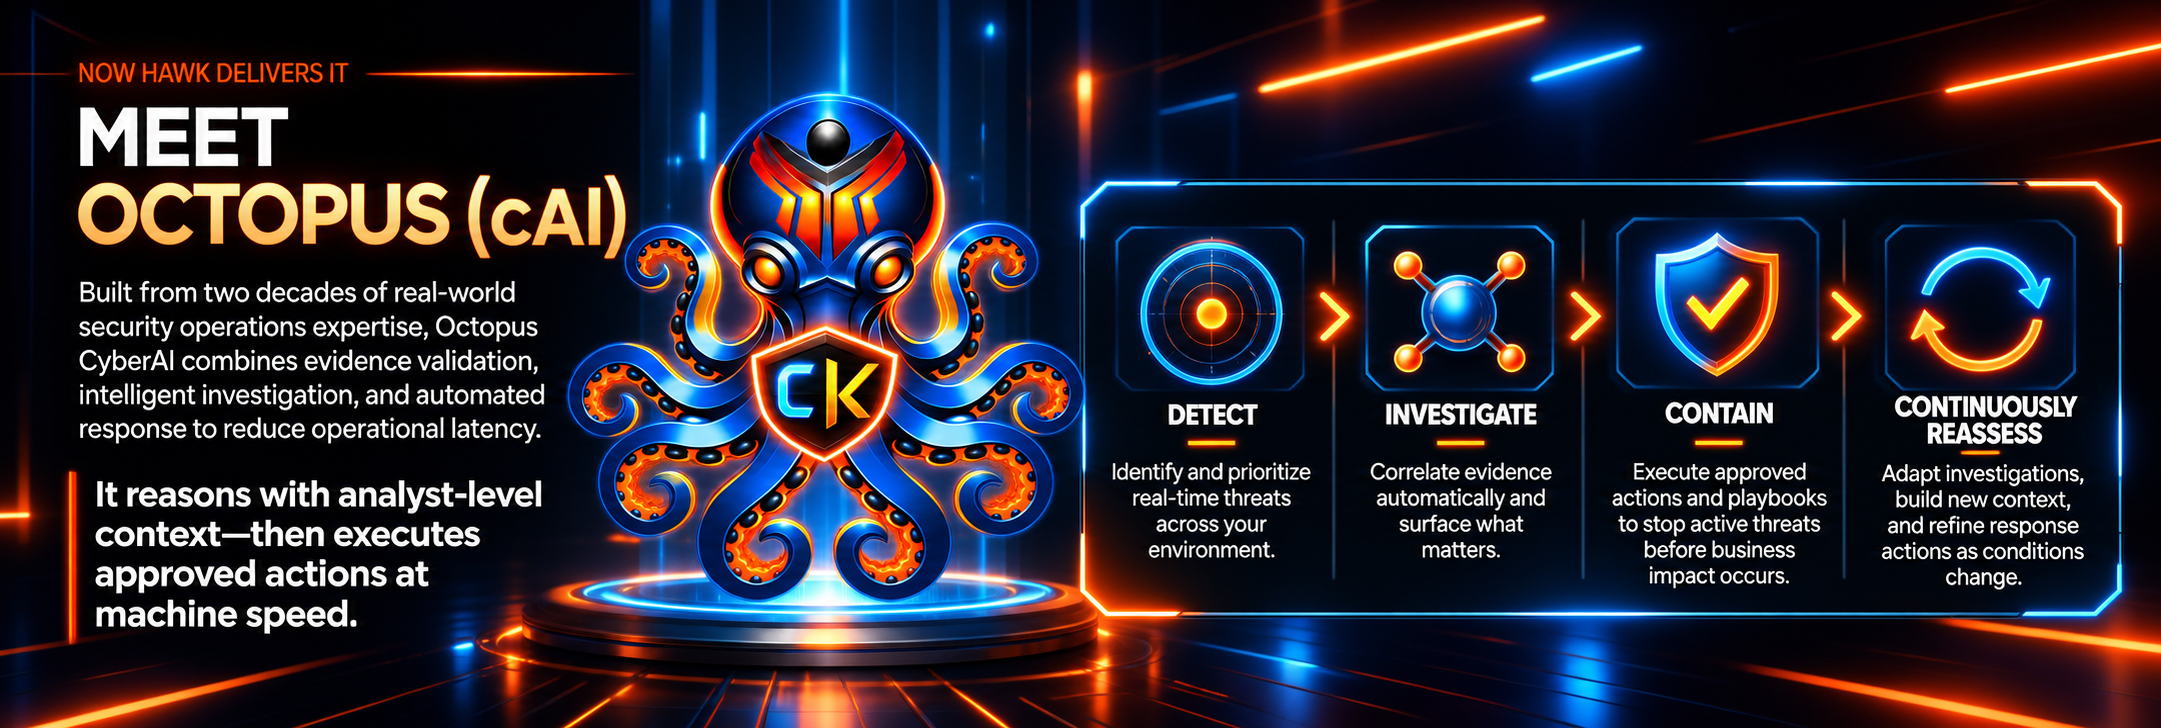
HAWK.io works with the security technologies organizations already own to extend security operations beyond log management, detection, and alerting. vTTAC™ enriches security telemetry with additional host and operational context, ClaimKit identifies, extracts, and cites relevant evidence, and Octopus cAI autonomously investigates, reasons across that evidence, and validates findings.
Together, these capabilities help reduce manual investigation and response work, accelerate decision-making, and move validated threats toward authorized containment without requiring organizations to replace their existing SIEM or security stack.
Real-time visibility → enriched context → evidence-driven autonomous investigation → authorized containment → measurable outcomes
Evidence-Driven Security Operations
vTTAC™ enriches security telemetry with host, identity, endpoint, and operating-system context. ClaimKit identifies, extracts, and cites the evidence relevant to an investigation. Octopus cAI uses that focused evidence to autonomously investigate, reason, correlate activity, and validate findings.
Together with HAWK Engine analytics and policy-governed response, these capabilities help organizations move from real-time detection through investigation and containment without depending on a chain of manual security processes.
Evidence Intelligence for Autonomous Security Investigation
ClaimKit transforms security data into focused, traceable evidence for faster and more accurate security investigations. It identifies, extracts, and cites the evidence relevant to an investigation, reducing the amount of information that must be processed before security activity can be understood and validated.
ClaimKit gives Octopus cAI a focused evidence set for autonomous investigation, reasoning, and validation. Together, ClaimKit and Octopus cAI help HAWK.io move from security signals to evidence, investigation, decisions, and coordinated response with greater speed and confidence.
Relevant evidence → autonomous investigation → validated findings → coordinated response
From Detection to Containment Before Business Impact
Security operations should not stop at detection. HAWK.io helps organizations establish what happened, identify what matters, determine the appropriate response, and execute authorized actions before a threat becomes a larger business event.
HAWK.io extends your existing security stack with patented technology to enable machine-speed security operations that reduce decision latency, improve security maturity, and deliver stronger outcomes—without requiring you to replace your current tools.
Real-time detection. Evidence-driven autonomous investigation.
Coordinated containment. Measurable security outcomes.